wireless internet providers
Absorbable Modified Polymers Technology, Advanced Technology Grants Pass, Aidan'S Professional Technology Services, Albuquerque Nm Information Technology Recruiters, Bhd Technology Vr, Catholic "Information Technology, Ceo Comcast Technology, Computer Technology Electronic, Current Applications Of Rdna Technology, Disadvantages Technology Law, Ferrum Technology Services, Fundamentals Of Medical Laboratory Technology, Gmu Department Of Information Technology, Hornborg Alf Technology Effects, I'M Done Working In Technology, James V. Arms Technology, Jurassic Park Technology Analysis, Liquidmetal Technology News, Llc, Mathey Technology And Engineering, Medical Technology In 500 Bc, Musc Library Technology Downloads, New Jersey Technology Office Space, Pc Ralley Technology, Ridge Technology Services, Technology 3x Reverse Etf, Technology Abuse Use, Technology Adoption Three Types, Technology Advantage Info, Technology And Improving Menial Jobs, Technology Classroom Building 311, Technology Companys In Usa, Technology Distracting Studying Students, Technology Docking Stations, Technology Enablement White Paper, Technology Images For Ppt, Technology Impact On Finance Departments, Technology In Chennai, Technology In Greek Translation, Technology Into History Lesson, Technology Is Electricity Ted Talks, Technology Professionals Of British Columbia, Technology Relatesecuirty Topics, Technology Studies Emu, Technology To Prevent Medication Errors, Technology Want What Ails Look, Tesla Technology Roadmap, Veterinary Assisting Vs Veterinary Technology, Wentworth Institute Of Technology Animation, What Is Today'S Technology, With The Arise Of Technology
Jeffrey Cuebas
0 Comments
This code hacks nearly every credit card machine in the country
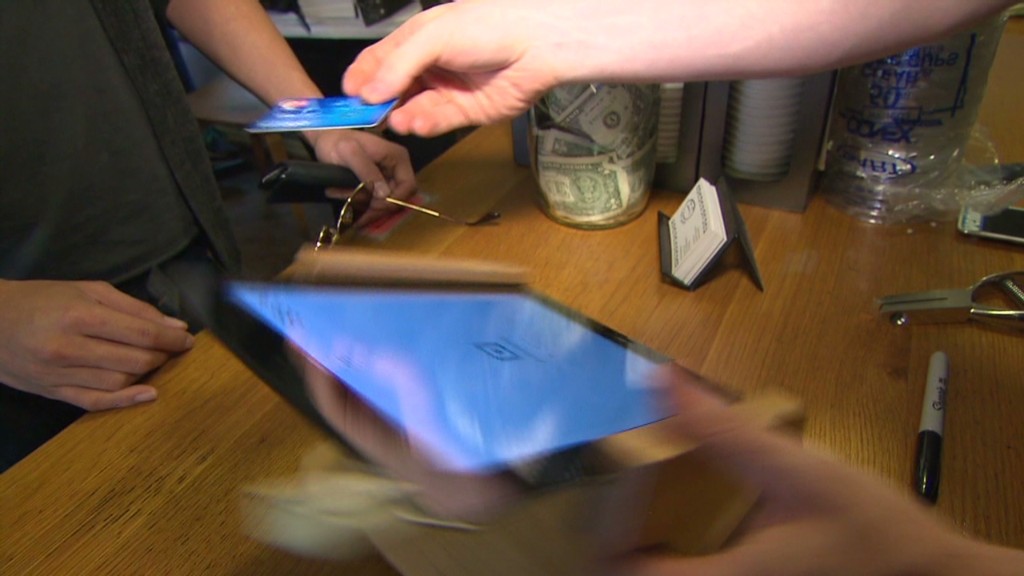
Get all set for a facepalm: 90% of credit history card viewers at this time use the identical password.
The passcode, established by default on credit card machines because 1990, is quickly discovered with a swift Google searach and has been uncovered for so prolonged there is certainly no feeling in hoping to cover it. It’s either 166816 or Z66816, depending on the device.
With that, an attacker can gain full handle of a store’s credit history card readers, possibly allowing for them to hack into the equipment and steal customers’ payment data (consider the Target (TGT) and Dwelling Depot (Hd) hacks all over once again). No surprise large retailers hold getting rid of your credit card knowledge to hackers. Stability is a joke.
This most up-to-date discovery arrives from researchers at Trustwave, a cybersecurity agency.
Administrative obtain can be employed to infect devices with malware that steals credit card information, discussed Trustwave executive Charles Henderson. He in-depth his results at last week’s RSA cybersecurity meeting in San Francisco at a presentation named “That Issue of Sale is a PoS.”
Take this CNN quiz — uncover out what hackers know about you
The dilemma stems from a match of very hot potato. Gadget makers provide machines to specific distributors. These sellers offer them to merchants. But no one particular thinks it is really their task to update the learn code, Henderson advised CNNMoney.
“No 1 is switching the password when they established this up for the first time everyone thinks the security of their point-of-sale is anyone else’s duty,” Henderson reported. “We are earning it quite effortless for criminals.”
Trustwave examined the credit score card terminals at extra than 120 suppliers nationwide. That involves important clothes and electronics merchants, as perfectly as community retail chains. No distinct retailers were being named.
The huge vast majority of equipment have been created by Verifone (Pay out). But the very same situation is existing for all main terminal makers, Trustwave mentioned.
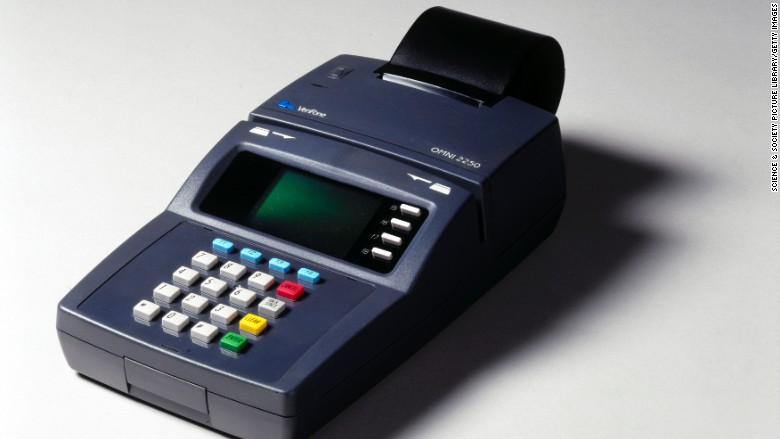
A spokesman for Verifone claimed that a password by itself is just not sufficient to infect machines with malware. The organization reported, right up until now, it “has not witnessed any assaults on the protection of its terminals based mostly on default passwords.”
Just in scenario, however, Verifone claimed suppliers are “strongly recommended to transform the default password.” And at present, new Verifone equipment occur with a password that expires.
In any scenario, the fault lies with suppliers and their particular sellers. It is really like home Wi-Fi. If you purchase a residence Wi-Fi router, it truly is up to you to alter the default passcode. Merchants need to be securing their possess machines. And equipment resellers must be encouraging them do it.
Trustwave, which assists shield stores from hackers, stated that preserving credit history card devices protected is very low on a store’s record of priorities.
“Businesses spend extra dollars picking the coloration of the level-of-sale than securing it,” Henderson claimed.
This issue reinforces the conclusion produced in a new Verizon cybersecurity report: that stores get hacked mainly because they are lazy.
The default password factor is a significant problem. Retail pc networks get exposed to laptop or computer viruses all the time. Contemplate a person case Henderson investigated not too long ago. A terrible keystroke-logging spy software package finished up on the computer a retail store works by using to process credit card transactions. It turns out staff members experienced rigged it to participate in a pirated model of Guitar Hero, and unintentionally downloaded the malware.
“It demonstrates you the degree of obtain that a whole lot of people today have to the stage-of-sale environment,” he said. “Frankly, it can be not as locked down as it should be.”
CNNMoney (San Francisco) Very first posted April 29, 2015: 9:07 AM ET